Sysdig vs. CrowdStrike Falcon Cloud SecurityKeep your EDR. Your clusters need more than a summary.
Sysdig runs alongside what you already have, and gives your responders the capture, not just the conclusion.


Why Sysdig Is a Better Choice Than
Falcon Cloud Security
Five questions to ask before you renew
Sysdig is a platform, not a portfolio. Detection, posture, vulnerabilities, and identity all read from the same runtime data, so your team works the short list of what’s actually running rather than the whole scan. Headless exposes it through MCP and APIs, so the answers land in the tools your team already uses.
sysdig
falcon cloud security
sysdig vs. falcon cloud security
Why Sysdig is a better choice than
Falcon Cloud Security
Can you replay the attack?
Every detection ships with evidence. Syscall-level capture and full process trees, replayable after the fact.
Strong at the exploit. Thin on the lead-up. No syscall capture, so reconstruction depends on what the sensor already decided to keep.
Day one, or day ninety?
Protected on day one. Falco rules ship on by default, no learning period.
Ninety days of learning first. Policies must be switched on by an admin, then the platform needs a learning cycle to reach full protection.
Can you read the rule?
Every rule is public. Falco is CNCF graduated, on GitHub, yours to change.
You can write policy. You can’t read the engine. Custom Rego rules govern compliance. The detection logic itself has never been published.
Do your rules come with you?
Your Falco rules keep working. Same open engine, with Threat Research curation on top.
Your Falco rules don’t come with you. Switching means rewriting your detection logic with theirs.
Ranked by your risk, or the world’s?
Ranked by what’s loaded in your environment. Not what’s exploitable somewhere in general.
Ranked by exploitation likelihood. Adversary tradecraft and threat intelligence, not whether the code is actually loaded where you run it.
Interactive tour
Check the answers yourself.
No form, and nothing to install.
Or have an engineer run it on your environment
GOLDMAN SACHS WITH SYSDIG
At our scale, it is important to have a complete record, even if the containers last only a few seconds. We need to be able to capture this data at scale to conduct not only forensics investigations, but also security audits.
Wes Williams, Global Head of Security Incident Response, Goldman Sachs
Goldman Sachs runs Sysdig across more than 180,000 hosts, multi-cloud and on-prem, polling millions of containers per second.
Read Goldman Sachs’ story
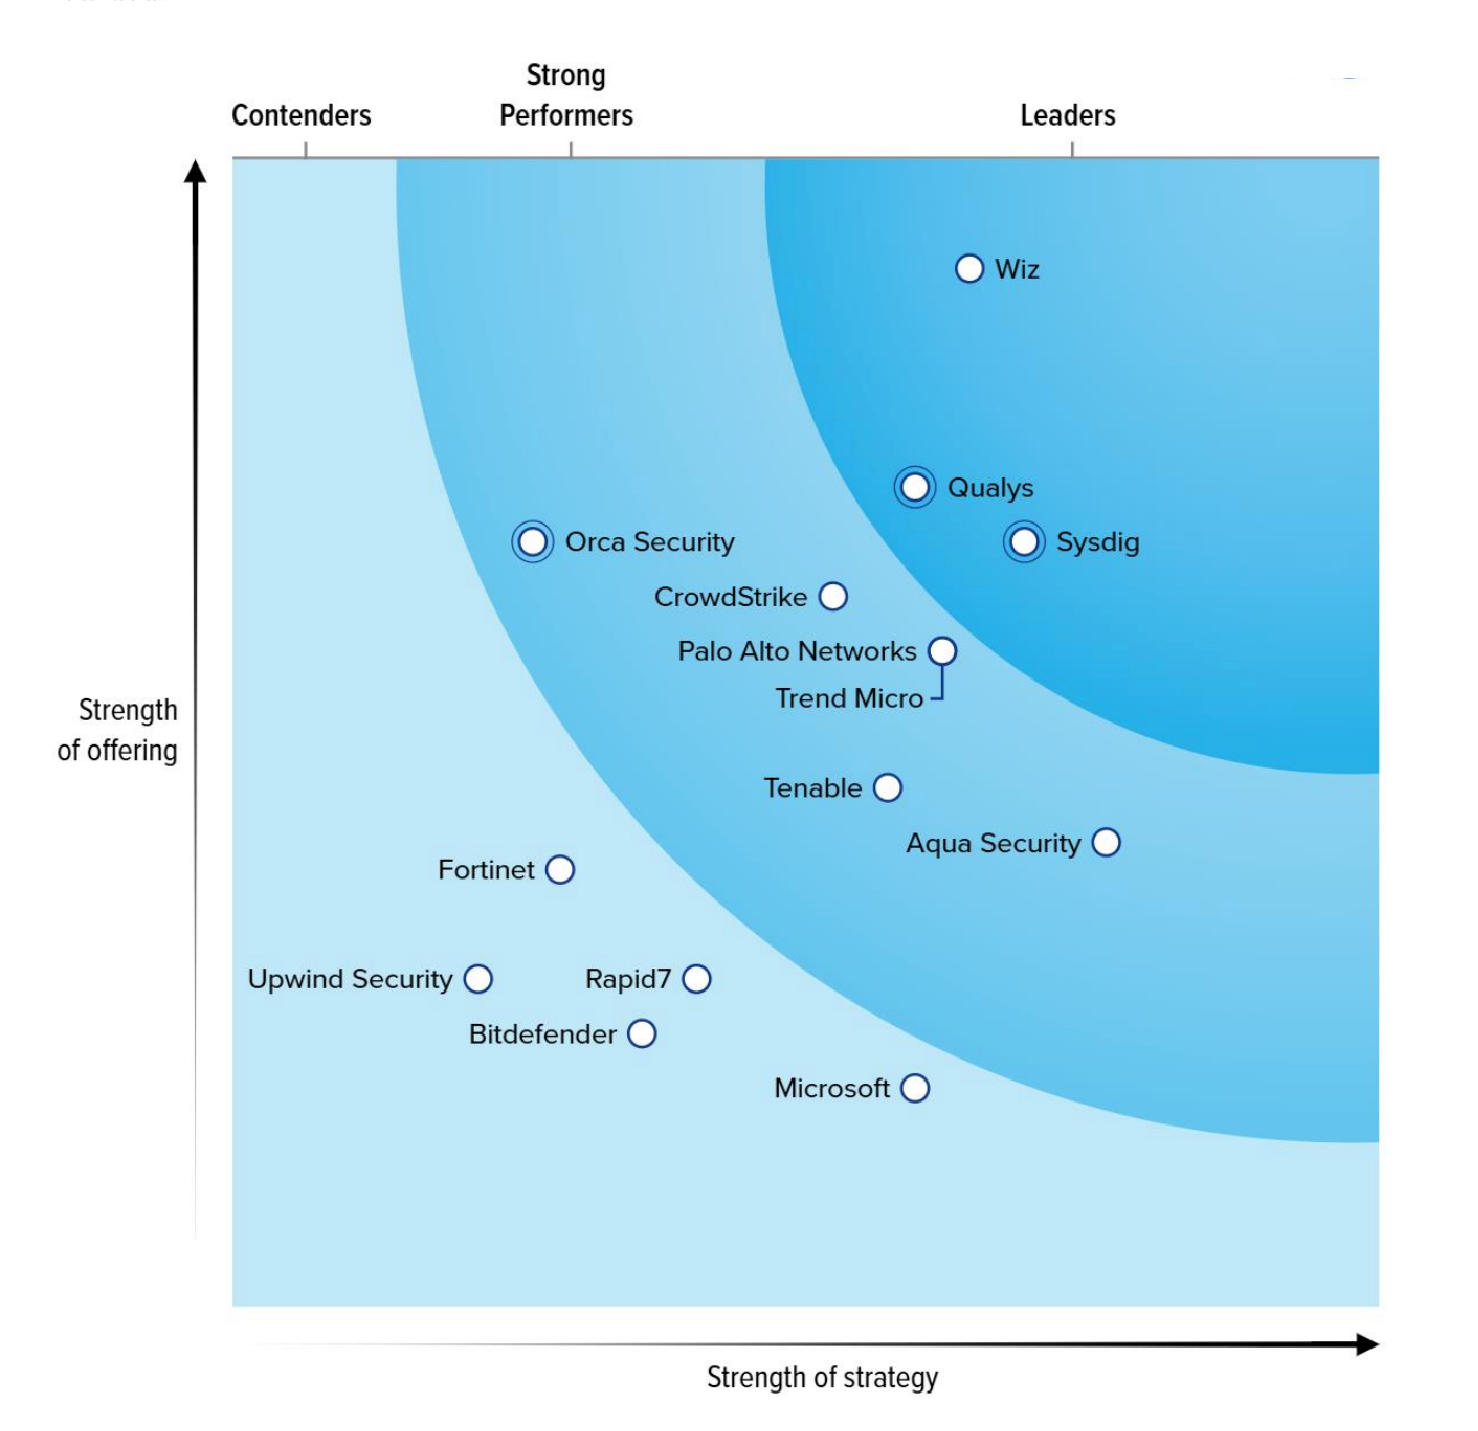
3 teams, 1 platform
SRE, SOC, and Threat Hunting all run on Sysdig
180K+
hosts, multi-cloud and on-prem
Millions
of containers polled per second
Overlap offer
Free Sysdig for every month left on your CrowdStrike Falcon Cloud Security contract.
Claim your free months
We match Sysdig to whatever’s left on your CrowdStrike term.