

Automate & accelerate security response
Torq offers an AI SOC Platform that helps security teams triage, investigate, and respond to threats faster.
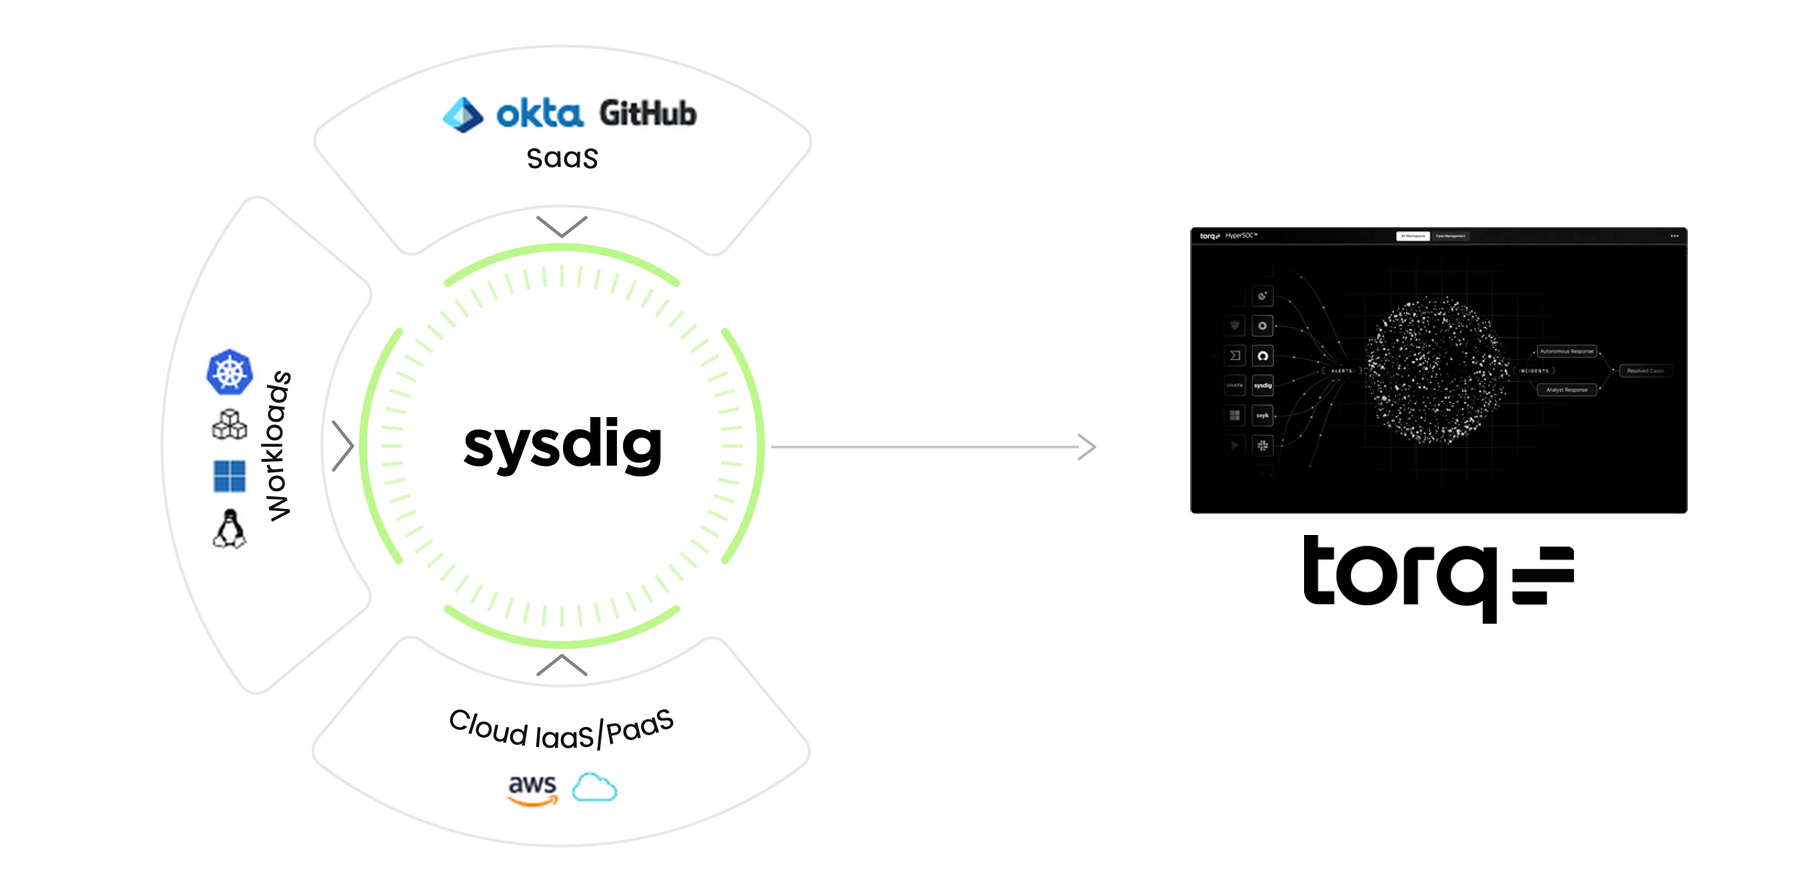
Sysdig and Torq help security teams turn real-time cloud threat detection into fast, context-rich response workflows. Sysdig identifies suspicious activity across cloud workloads, containers, and Kubernetes environments and Torq uses those signals to enrich investigations and orchestrate response.
With ready-to-use and customizable workflows, teams can triage alerts, create and assign cases, gather evidence, notify stakeholders, and trigger approved remediation actions without stitching together manual processes.
Customer Value
- Accelerate detection to response: Move from alert to triage and case enrichment in seconds.
- Enrich every investigation: Add container, image, vulnerability, workload, namespace, and cloud context to each event.
- Automate case management: Create, triage, enrich, and assign tickets to the right team and user.
- Reduce repetitive SOC work: Replace manual lookups and handoffs with automated investigation workflows.
- Respond with confidence: Use Sysdig runtime context to guide approved mitigation and response actions.
- Adapt to your SOC: Customize out-of-the-box playbooks or build purpose-built workflows with Torq and Sysdig APIs.
Learn more
Check out our blog on Sysdig + Torq for additional insights into this powerful security and response combination.
SIEM/SOAR